Picture a one-person business on an ordinary Tuesday. The phone that holds the authenticator app slides off a café table and cracks, and the laptop's password manager wants a code that only that phone can provide. Then the Google Workspace account that receives every invoice, password reset and client email starts asking for verification the owner can no longer supply. By lunchtime the website is still up, but the person who runs it cannot reach a single administrative screen.
Passkeys have made sign-in safer and faster for millions of people, and that progress is real. The weak point for a solo site owner has moved, though, from the password itself to the recovery chain behind it. That chain runs through registrar, DNS, email, hosting and CMS logins, and each one quietly depends on another. Planning that chain in advance is the single most useful security habit a small operator can build this year.
This guide covers where passkeys stand and what federal guidance says about the passwords you still have. It then builds a lockout plan that survives the loss of one device or one inbox.
Passkeys Went Mainstream in 2026
The FIDO Alliance, the industry body behind the passkey standard, published its State of Passkeys report on May 7. Its consumer survey of 11,000 adults across ten countries found that 90 percent were aware of passkeys and 75 percent had enabled one on at least some accounts. Nearly half, 49 percent, used them regularly when a site offered the option. The alliance also estimates that about five billion passkeys are now in use, a figure it presents as its own estimate rather than a survey result.
"Passkeys are moving into the mainstream because they deliver something the industry has struggled to achieve for decades," said Andrew Shikiar, the alliance's executive director and CEO. He identified that benefit as authentication that is both more secure and easier to use.
In a May 7 post on the company's security blog, Vasu Jakkal and Nadim Abdo wrote that "Passwords remain a major source of risk; they're difficult to manage and easy to steal." The post also said that beginning in January 2027, security questions will be removed as a password reset option in Entra ID. The same post acknowledged the weak spot that matters most here, noting that account recovery has historically been vulnerable to attackers who try to hijack the process.
The threat picture for small businesses explains why both trends matter at once. Verizon's 2026 Data Breach Investigations Report, released May 19, included a snapshot of 7,256 incidents at small and medium businesses. In that group, credentials were the compromised data in 31 percent of breaches, and credential abuse was the initial way in for 13 percent. Exploited software vulnerabilities now lead overall, which is why patching still matters, but stolen logins remain a cheap and common route into a small company.
What NIST Now Says About the Passwords You Still Have
Not every account supports passkeys yet, so the remaining passwords deserve current rules rather than habits from 2010. The National Institute of Standards and Technology finalized its digital identity guidelines, NIST SP 800-63B-4, in 2025, and several of its requirements overturn long-standing office folklore.
A password that serves as the only factor must be at least 15 characters, while one used alongside multi-factor authentication can be as short as eight, and systems should accept at least 64. The document states that "Verifiers and CSPs SHALL NOT require subscribers to change passwords periodically," reserving forced changes for cases where there is evidence of compromise, and it bans composition rules such as mandatory symbols. It also requires services to allow password managers and autofill, and it rules out security questions as a verification method.
For a solo operator, the practical translation is a long passphrase stored in a reputable password manager, multi-factor authentication wherever it is offered, and no calendar reminder to rotate passwords that have not leaked. Those three choices cover most of what the federal standard asks of individual users.
The Circular Trap at the Center of a Small Business
The most dangerous dependency for many small sites runs through Google Workspace or a similar hosted email suite. If the only super administrator on a Workspace account loses access, Google's administrator recovery process asks the owner to prove control of the domain by adding a CNAME record to its DNS. If the record is not found within 48 hours, the automated recovery fails. A support-assisted route also relies on a DNS record that can take up to 24 hours to propagate.
That requirement is reasonable on its face, but it creates a loop for anyone whose registrar account sends its password resets to an address on the same Workspace domain. Locked out of email, the owner cannot reset the registrar login, and without the registrar login, the owner cannot add the DNS record that would restore the email.
Google's own Recovery Contacts feature, launched in October 2025, does not close this gap. It lets a personal account name up to 10 trusted people who can confirm your identity. The help page is explicit, however, that "Google Workspace accounts can't have recovery contacts," which leaves business accounts dependent on administrative redundancy instead.
Google's published best practices for administrators supply that redundancy. The company advises that an organization "should have more than one super administrator account, each managed by a separate individual." It also recommends a separate everyday account for routine work, more than one enrolled security key and printed backup codes stored securely.
Domains Expire Quietly, and Email Goes With Them
The other single point of failure is the domain renewal. Under ICANN's Expired Registration Recovery Policy, registrars must send reminders roughly one month and one week before expiration and another notice within five days after it. They must also interrupt DNS resolution once the name lapses, which takes both the website and every address on the domain offline.
The policy guarantees the original owner at least eight consecutive days to renew before deletion, and generic top-level domain registries must then offer a 30-day redemption grace period. Many registrars provide longer windows, but eight days is the floor, and those reminder emails often land in an inbox that stopped working the moment DNS went dark.
We covered the DNS side of mail delivery in our guide to why contact form email disappears, and the same records that keep messages out of spam folders vanish the moment a domain lapses.
Building the Lockout Plan
Start by drawing the chain on a single page. Write down the registrar, the DNS host if it differs, the email provider, the web host and the CMS. Next to each one, record which email address and which second factor would recover it. Any arrow that loops back to an address on your own domain marks a place where one failure can cascade into several.
Next, move the registrar's recovery email to an address that lives somewhere else entirely, such as a personal account on a different provider. Turn on auto-renewal and confirm that the card on file has not expired. Then set your own calendar reminder a month before the renewal date, so the warning does not depend on the domain you are trying to protect.
Then add passkeys where the services support them, and pair each one with a backup that lives on a different device. GoDaddy's help documentation states that customers who use a passkey must add a backup verification method, and Porkbun has offered passwordless sign-in with security keys or device biometrics since 2023.
On Workspace, create a second super administrator account held by a person you trust, such as a business partner or bookkeeper. Keep your own daily email on a separate non-admin account. Enroll two hardware security keys on the admin login, store one away from your desk, and print the backup codes.
Personal Google accounts that still recover business logins should get Recovery Contacts now. Google gives an invited contact seven days to accept and then imposes a further seven-day wait before that contact can help. Waiting until the morning you are locked out is too late. The Inactive Account Manager on the same account lets you choose up to 10 people to receive data if the account goes unused for a period you set.
WordPress needs its own step, because core does not yet support passkeys. A Trac ticket requesting optional WebAuthn login was closed as a duplicate of an older request, with a maintainer noting there had yet to be any real discussion of adding it to core. Site owners who want hardware-key or biometric login use the Two Factor plugin with its WebAuthn provider add-on.
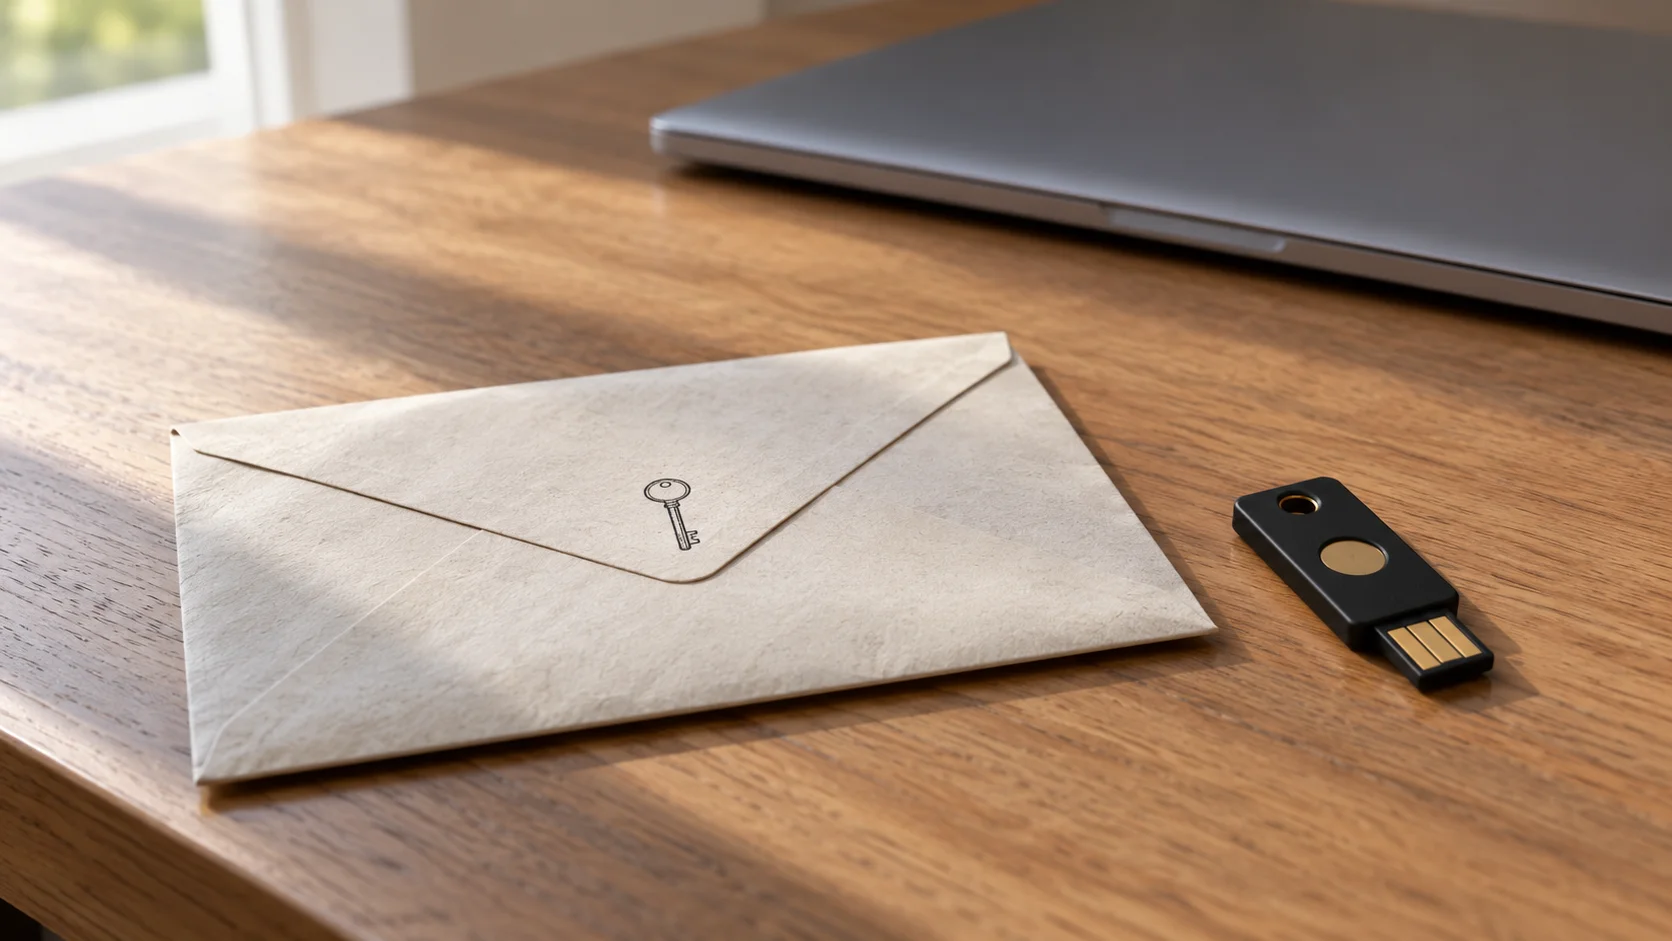
The final piece is a sealed break-glass sheet. Print the backup codes for the registrar, the email admin account and the host, then add the registrar account number and support phone line. Store the envelope somewhere a trusted person can reach it. Our earlier piece on running maintenance as a one-person operation makes the case for quarterly restore tests. The same slot is a good moment to open the envelope and confirm every code still works.
Why This Belongs Under Digital Wellbeing
Account lockouts rarely make headlines, but for a solo founder they arrive as a sudden loss of income, client trust and sleep. Verizon's report found that weak passwords and permission misconfigurations took almost eight months for half of the findings to be resolved, which suggests how easily this work slips behind more urgent tasks.
An afternoon spent mapping logins, moving one recovery address and printing a handful of codes costs far less than a week of support tickets with a registrar. The one-page diagram, a second admin and an envelope in a drawer are the pieces that let the owner recover from a cracked phone in an hour instead of a week.